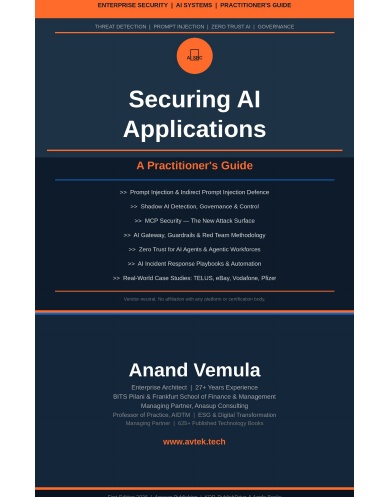
Securing AI Applications:
A Practitioner's Guide Prompt Injection, Zero Trust for AI, Shadow AI Governance, AI Red Teaming & Incident Response | 2026 Edition
Usually printed in 3 - 5 business days
AI is transforming how organizations operate — and how they are attacked. This practitioner's guide equips security engineers, architects, CISOs, and platform teams with the knowledge and frameworks needed to secure AI systems in production environments in 2026 and beyond.
What's Inside:
The AI Threat Landscape
Understand the new attack surface that AI creates: prompt injection, indirect injection, training data poisoning, agent privilege abuse, MCP tool compromise, context window manipulation, multi-agent trust chain attacks, and vector database poisoning. Includes an attack speed comparison showing why traditional defenses are no longer sufficient when attackers operate at machine speed.
Prompt Injection — The SQL Injection of the AI Era
Complete coverage of direct and indirect prompt injection attacks, multi-turn escalation, encoded injection, jailbreaking techniques, and the seven vectors through which indirect injection reaches AI systems: web pages, RAG documents, emails, code repositories, customer records, external APIs, and persistent agent memory. Includes defence-in-depth implementation guidance.
Securing the Agentic Workforce
Agent identity frameworks, task-based access control (TBAC), multi-agent trust chain risks (transitive trust abuse, orchestrator compromise, cross-agent injection, credential laundering), and permission model comparison (RBAC vs ABAC vs PBAC vs TBAC). Real-world lessons from TELUS's 100,000-employee agent platform deployment.
MCP Security — The New Attack Surface
Model Context Protocol security: malicious tool registration, tool description poisoning, package registry supply chain attacks, and eight specific security controls for securing MCP deployments. The MCP attack surface is the most underestimated emerging risk in enterprise AI.
Shadow AI — Detection, Governance & Control
Why shadow AI is more dangerous than shadow IT, five detection approaches (traffic analysis, DLP scanning, browser extension monitoring, network flow analysis, productivity tool analysis), and why the correct response is to out-design shadow AI rather than block it. Case study: Montclair State University.
Zero Trust for AI Systems
Applying Zero Trust principles to AI agents, models, and pipelines. Five-layer ZT architecture for agentic systems (identity, permissions, input validation, behavior monitoring, output inspection). Enterprise case studies: 20,000-user deployment across 8 business units; Swiss Post's journey from YOLO mode to
Details
- Publication Date
- Sep 11, 2026
- Language
- English
- Category
- Computers & Technology
- Copyright
- All Rights Reserved - Standard Copyright License
- Contributors
- By (author): Anand Vemula
Specifications
- Pages
- 52
- Binding Type
- Paperback Perfect Bound
- Interior Color
- Black & White
- Dimensions
- US Letter (8.5 x 11 in / 216 x 279 mm)